Turn Unstructured ReportingInto Actionable STIX Intelligence
The analyst-facing platform that transforms unstructured reporting, OSINT, and darknet signals into structured, searchable, relationship-rich threat intelligence. Extract facts, visualize relationships, and maintain full provenance for every insight.
Built for Security Analysts
The Threat Intelligence Platform continuously monitors global security research, using advanced NLP to automatically extract and structure data. Threat actors, malware, CVEs, IOCs, and darknet signals are immediately identified, normalized, and converted into STIX 2.1 objects.
The platform also maps relationships among infrastructure, TTPs, and campaigns while maintaining strict provenance back to the original source. Built for SOC teams that need to prioritize critical risks over irrelevant alerts, Threat Landscape cuts manual triage time by 50-70% and improves investigative depth.
Platform Features
Everything your security team needs to operationalize threat intelligence across open sources and darknet collection.
High-Fidelity Fact Extraction
Advanced NLP automatically extracts threat actors, malware families, CVEs, TTPs, and network indicators from unstructured reporting and converts narrative text into structured STIX 2.1 objects with verified entity recognition.
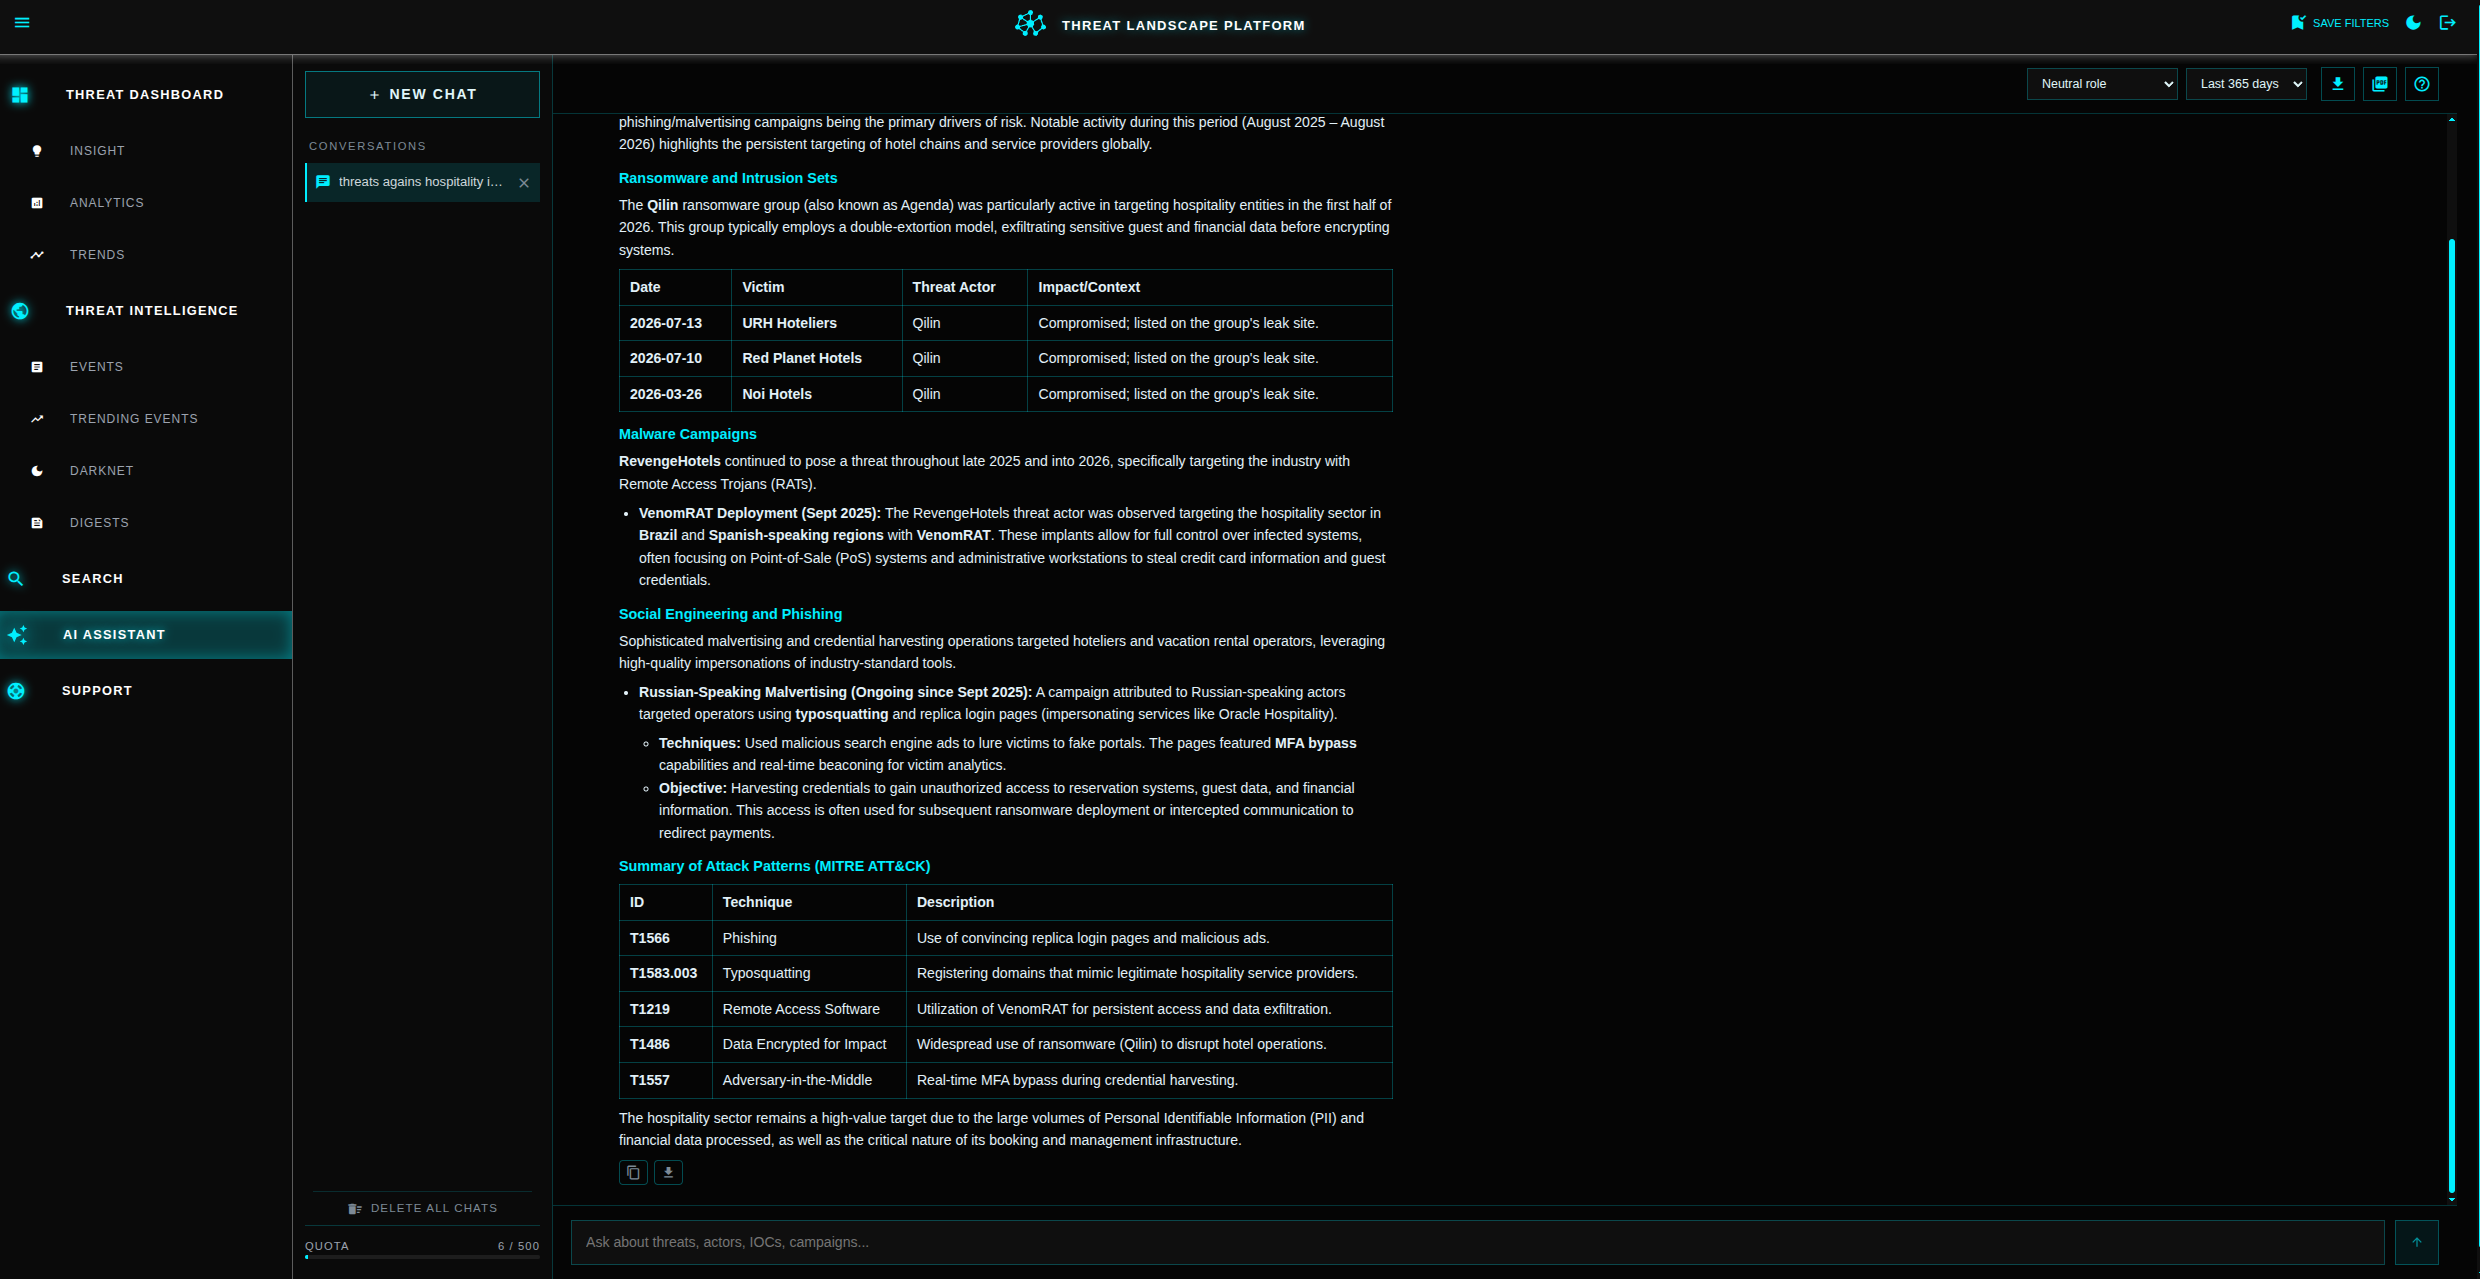
AI Assistant
A conversational assistant that runs on the same STIX knowledge store. Ask questions in plain English about threat actors, CVEs, malware families, and trends, and get role-aware answers fully grounded in the data, with no hallucination.
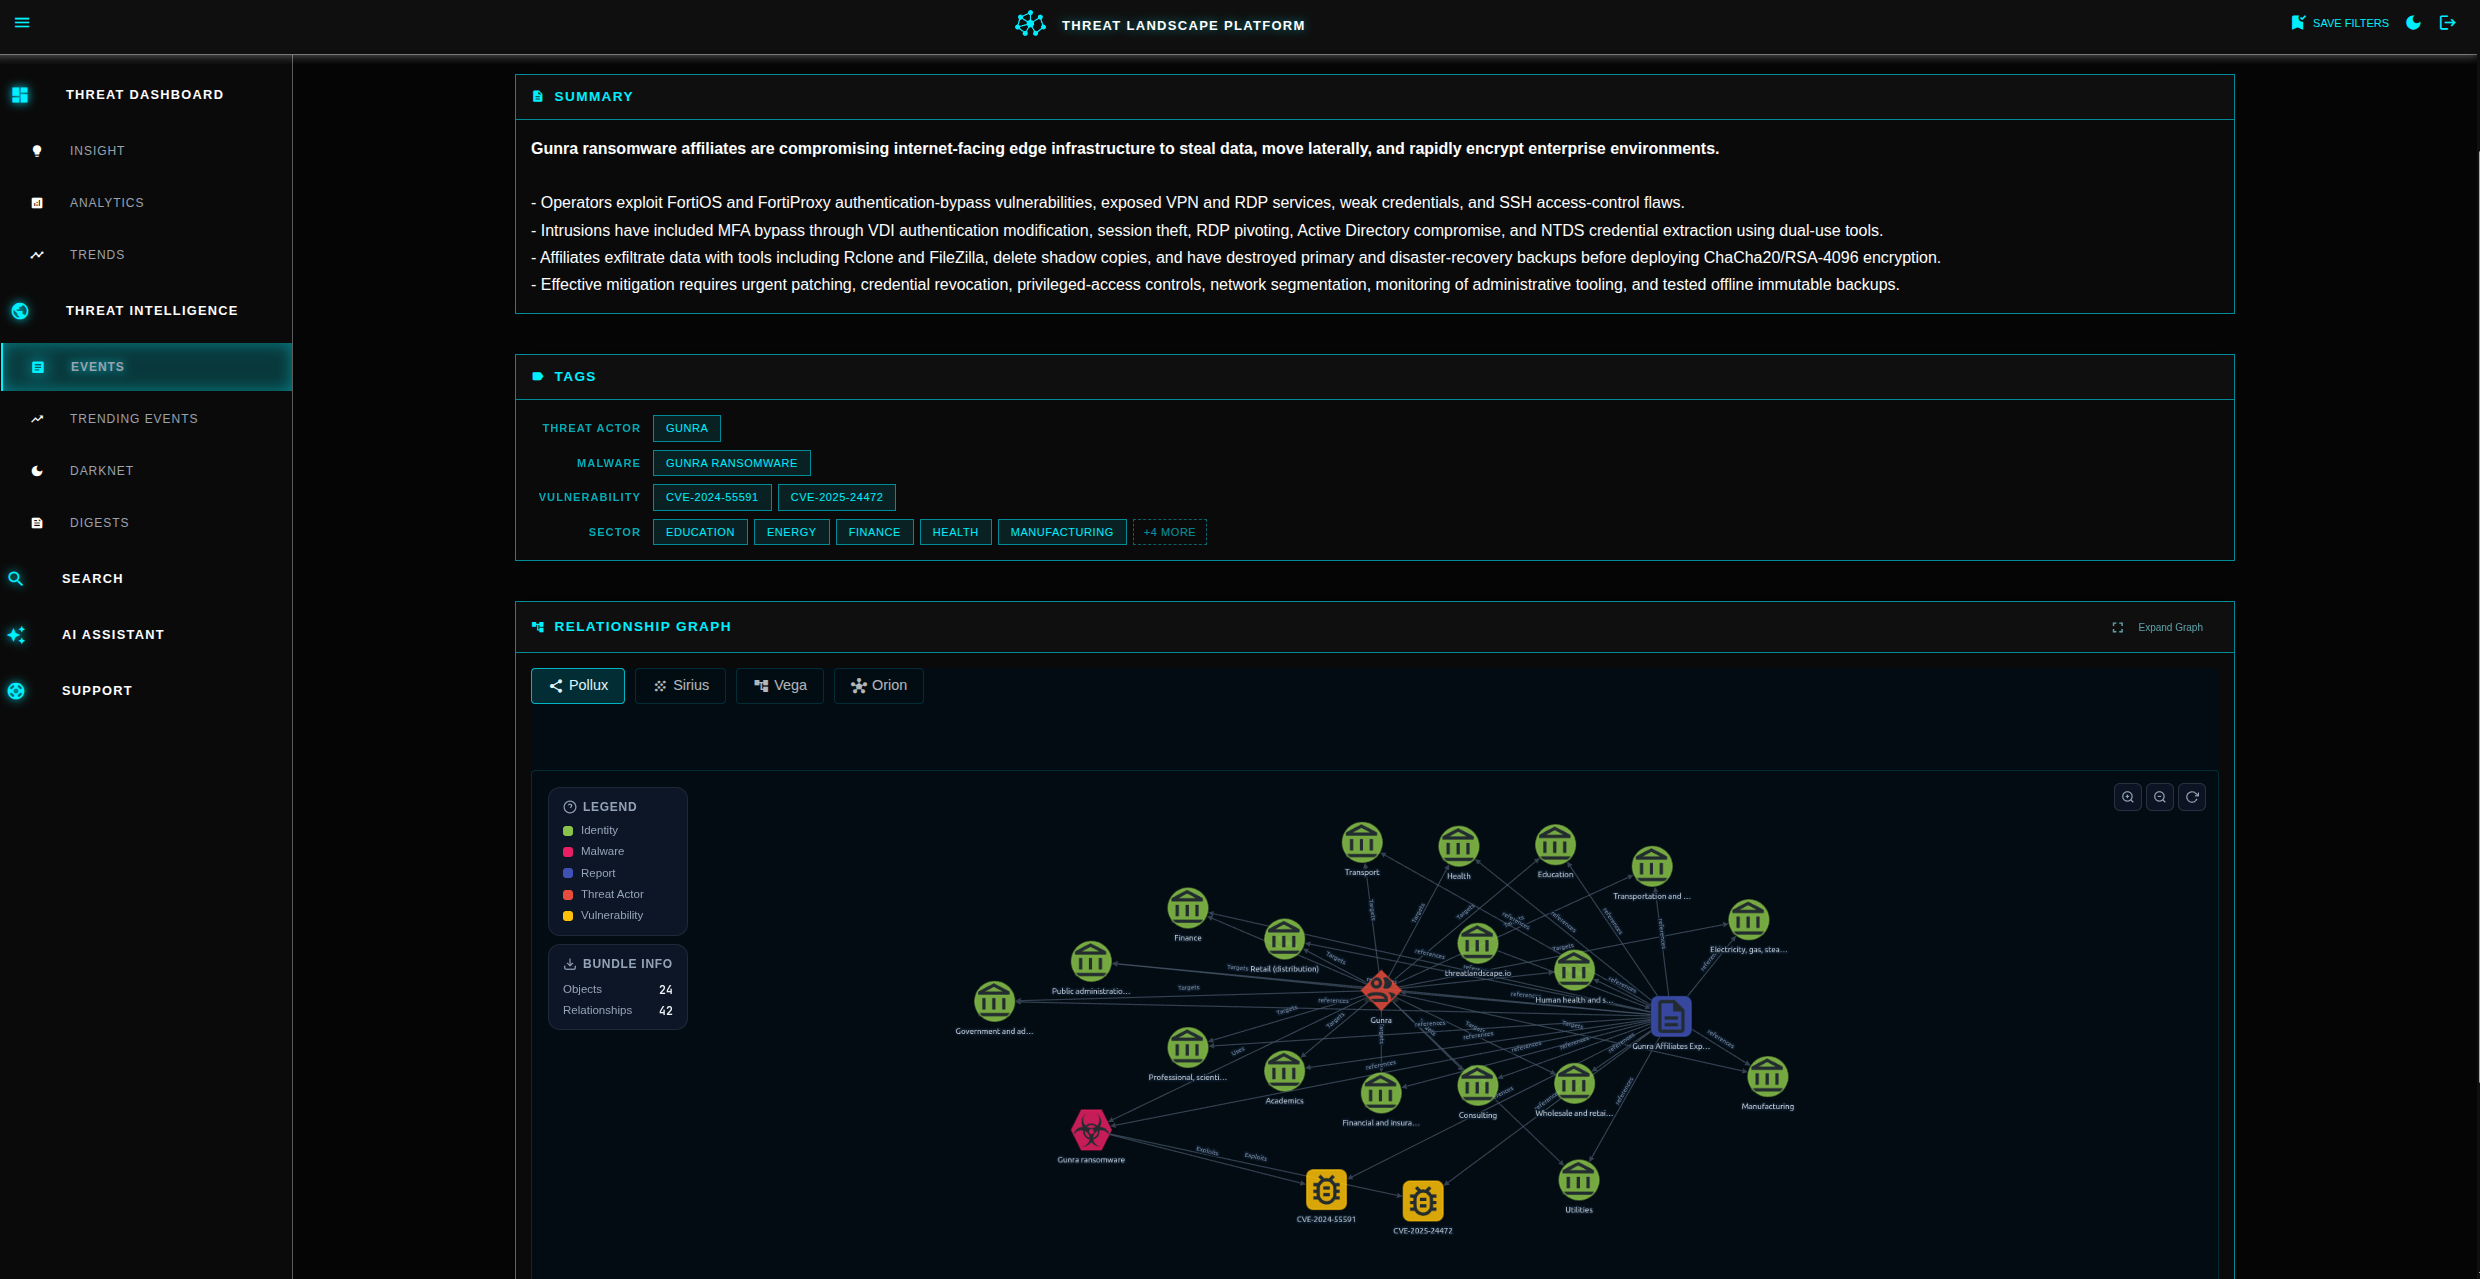
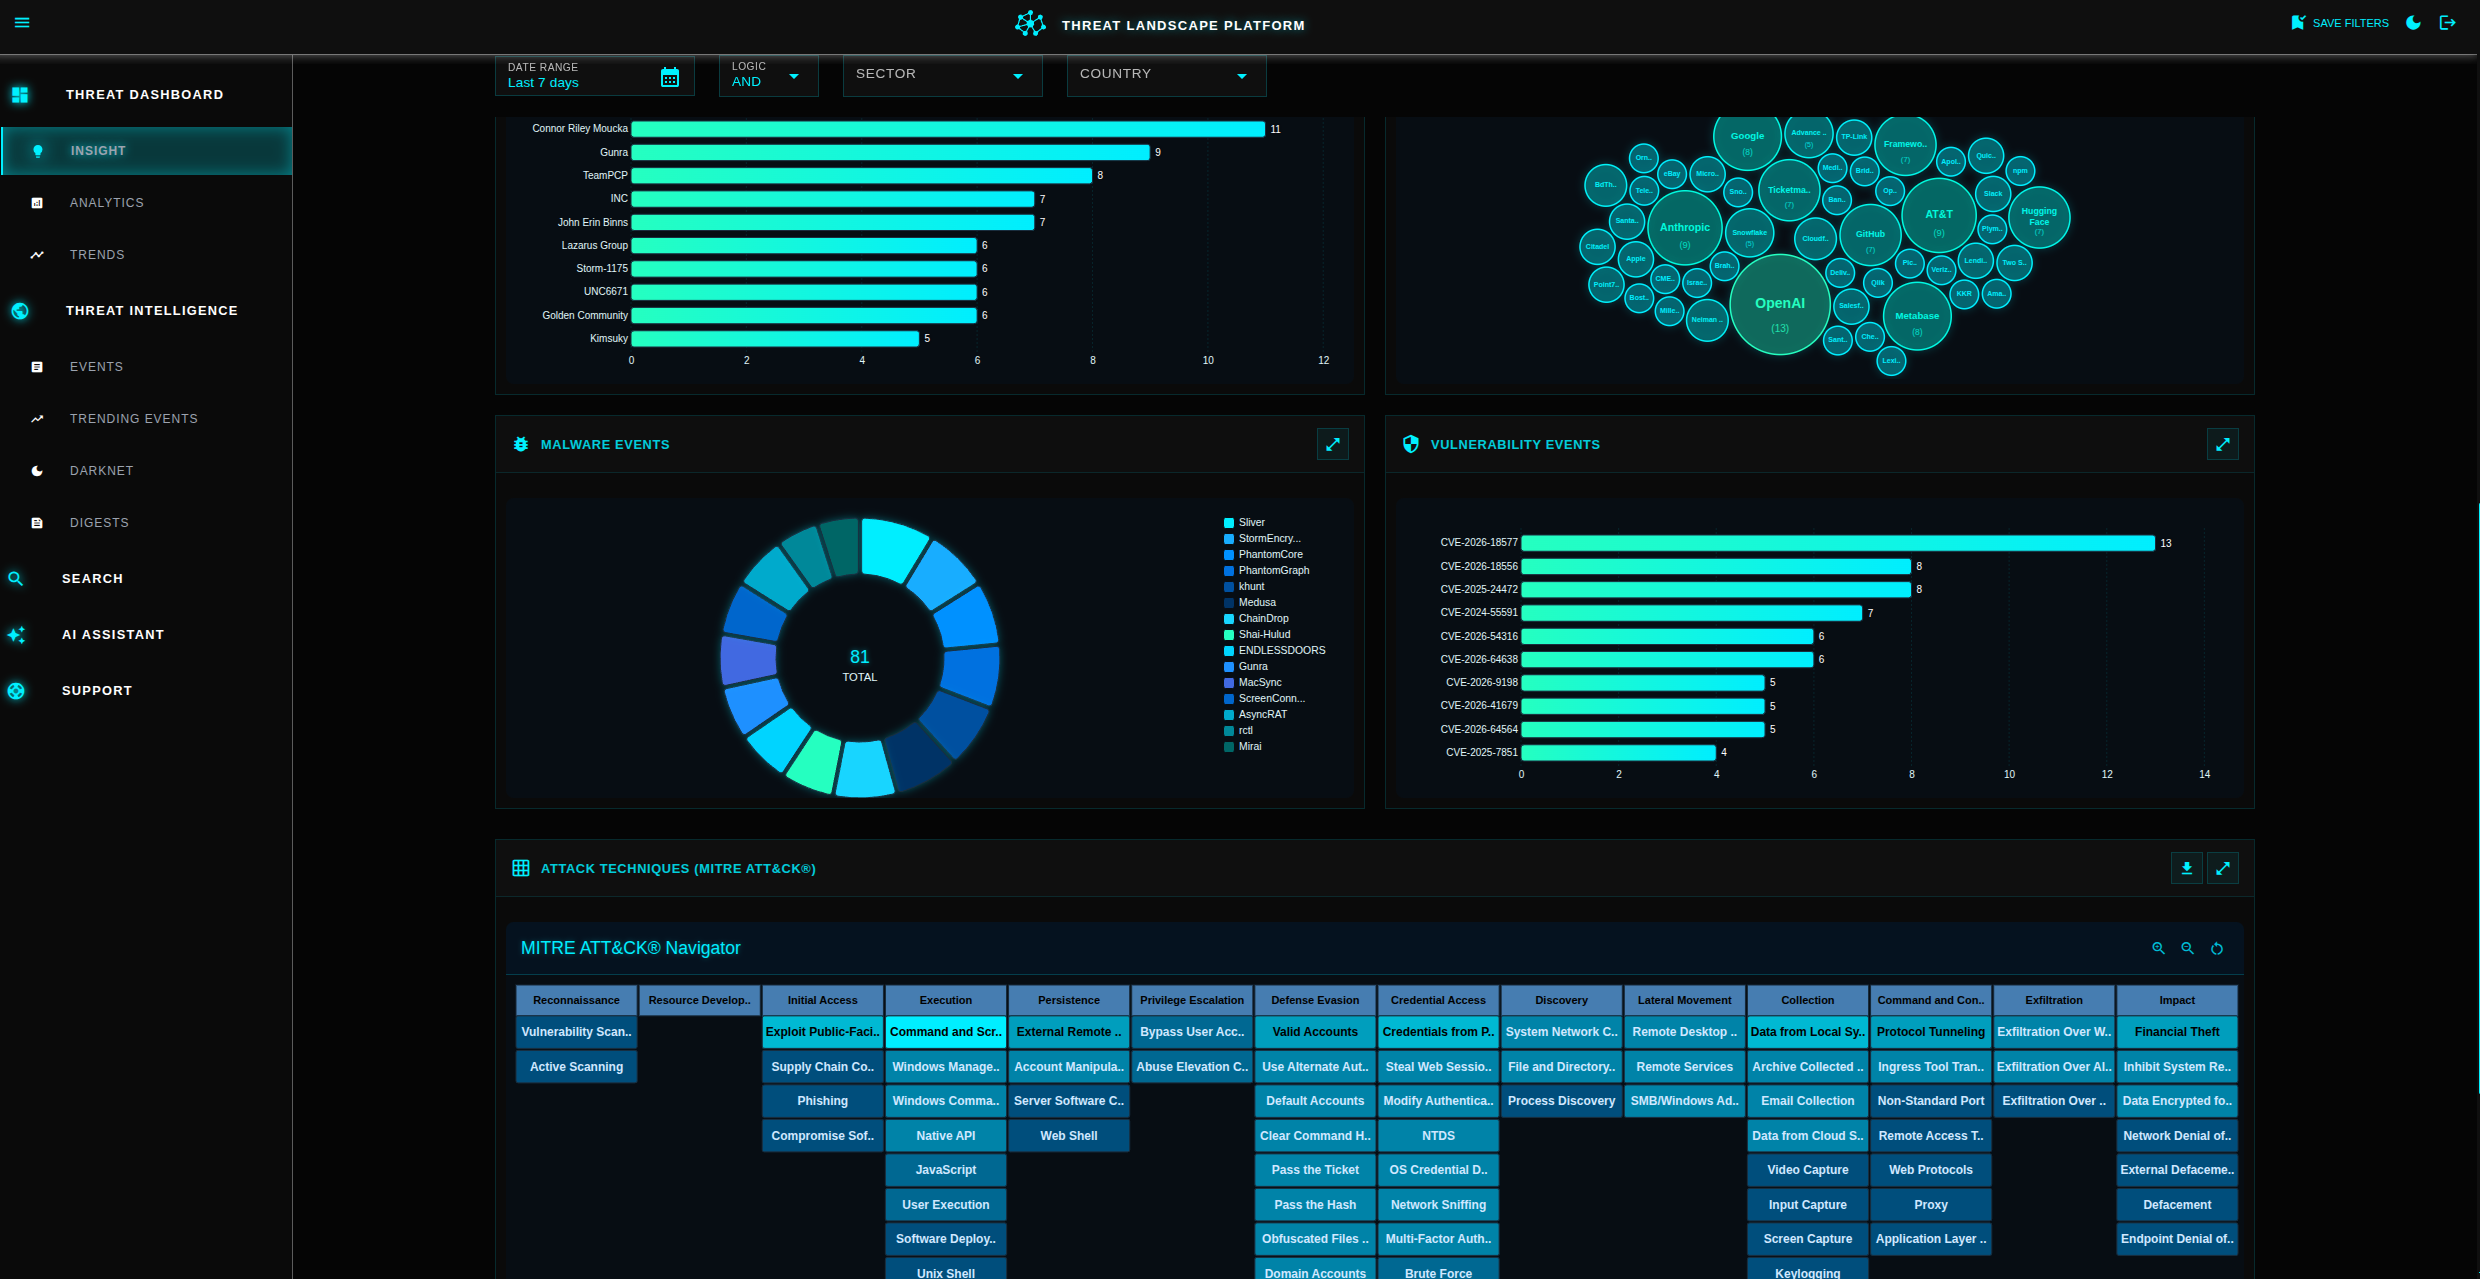
Visualized Threat Graph
Interactive graph visualization showing relationships between IOCs, threat actors, malware, and TTPs. See attack chains and actor infrastructure through MITRE ATT&CK framework mapping. Export directly to MITRE Navigator.
Full Provenance & Traceability
Every extracted fact keeps strict linkage to its source material via external_references, so analysts can validate intelligence authenticity, trace report origins, and maintain audit trails for compliance and investigative workflows.
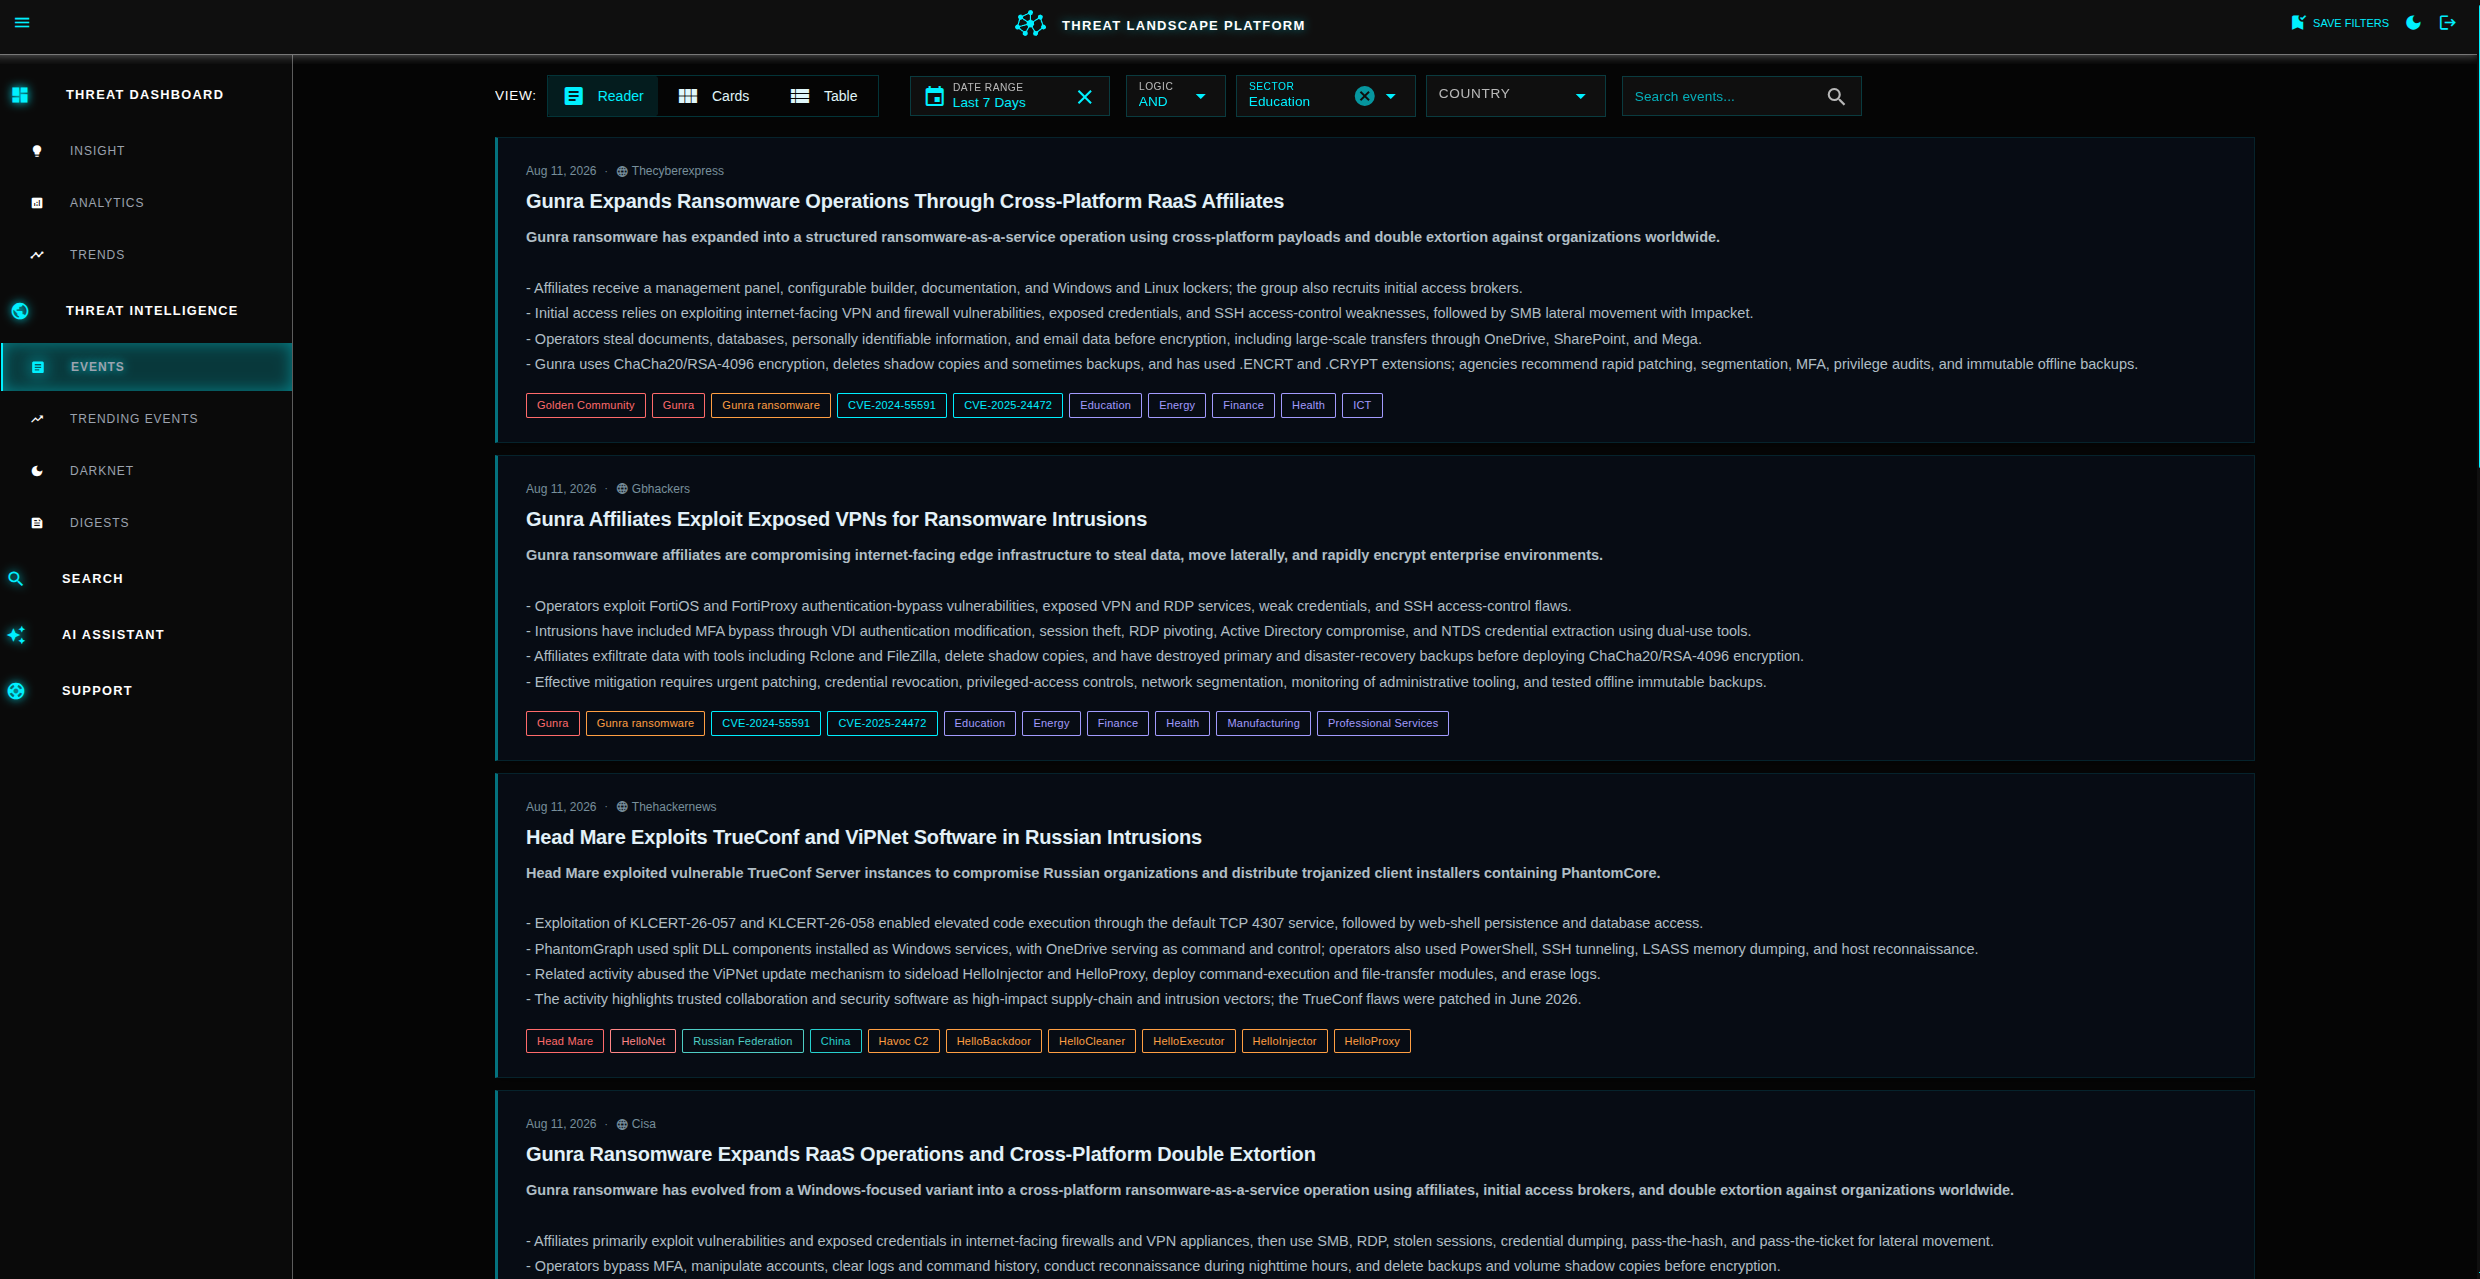
Advanced Search & Filtering
Multi-faceted search across threat actors, malware families, CVEs, TTPs, targeted sectors, and geographic regions. Filter by confidence levels, timeframes, and custom tags for precise intelligence retrieval.
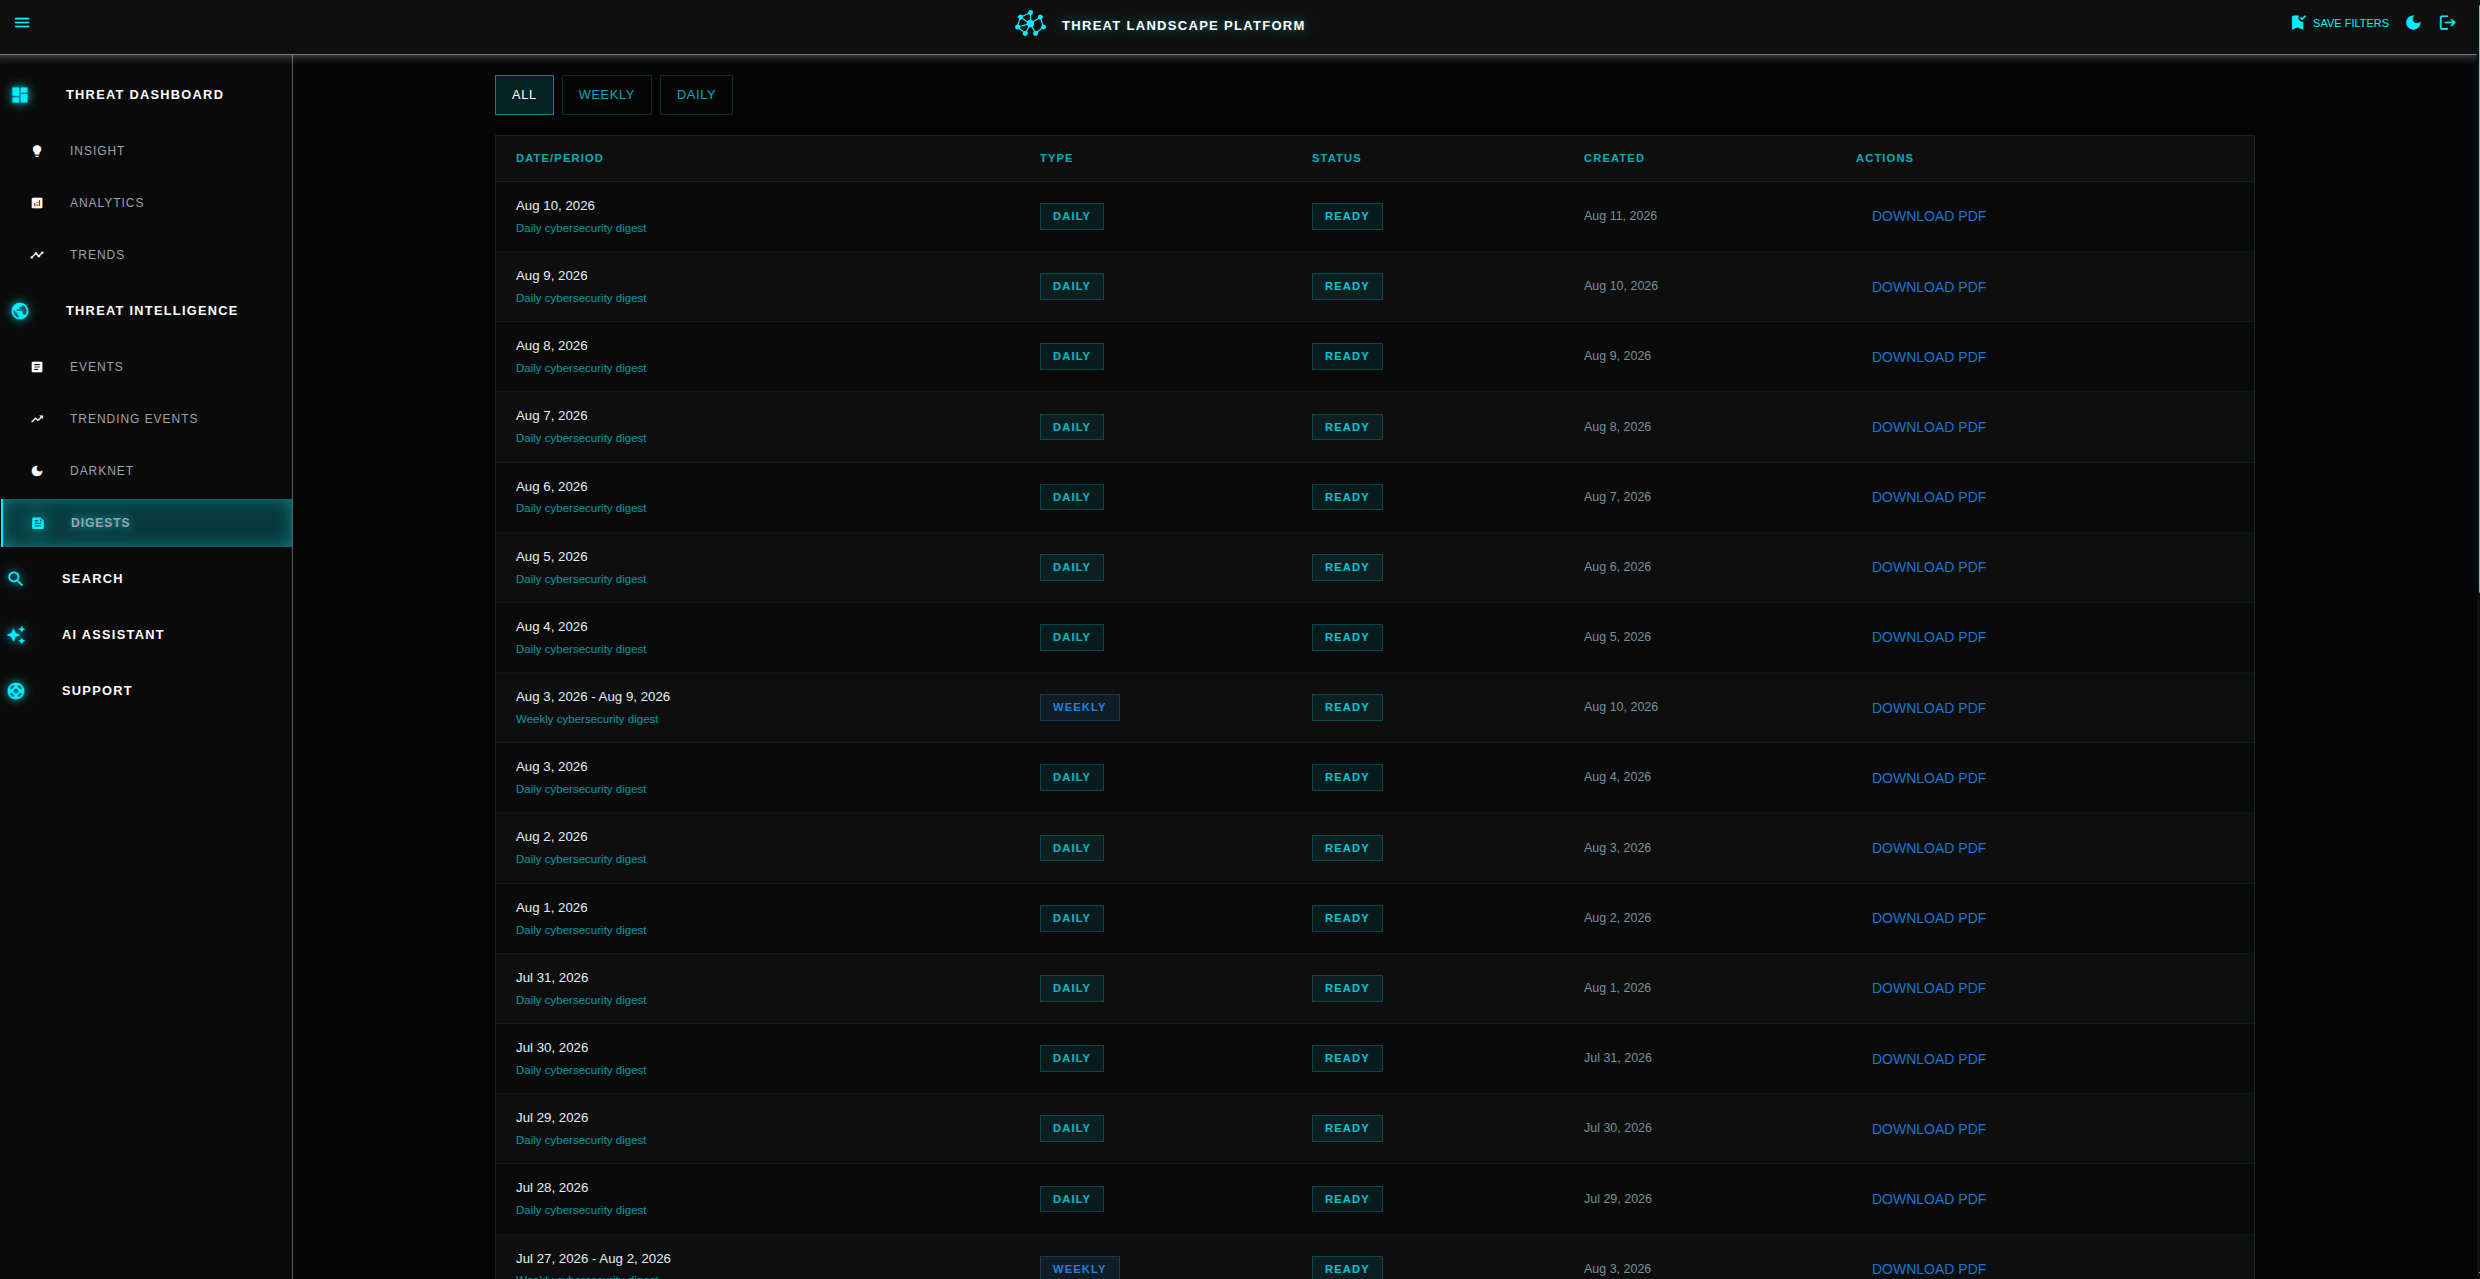
Daily & Weekly Intelligence Digests
Automated, analyst-curated intelligence summaries delivered on your schedule. Executive-ready reports on emerging threats, trending malware, new vulnerabilities, and the critical IOCs relevant to your organization.
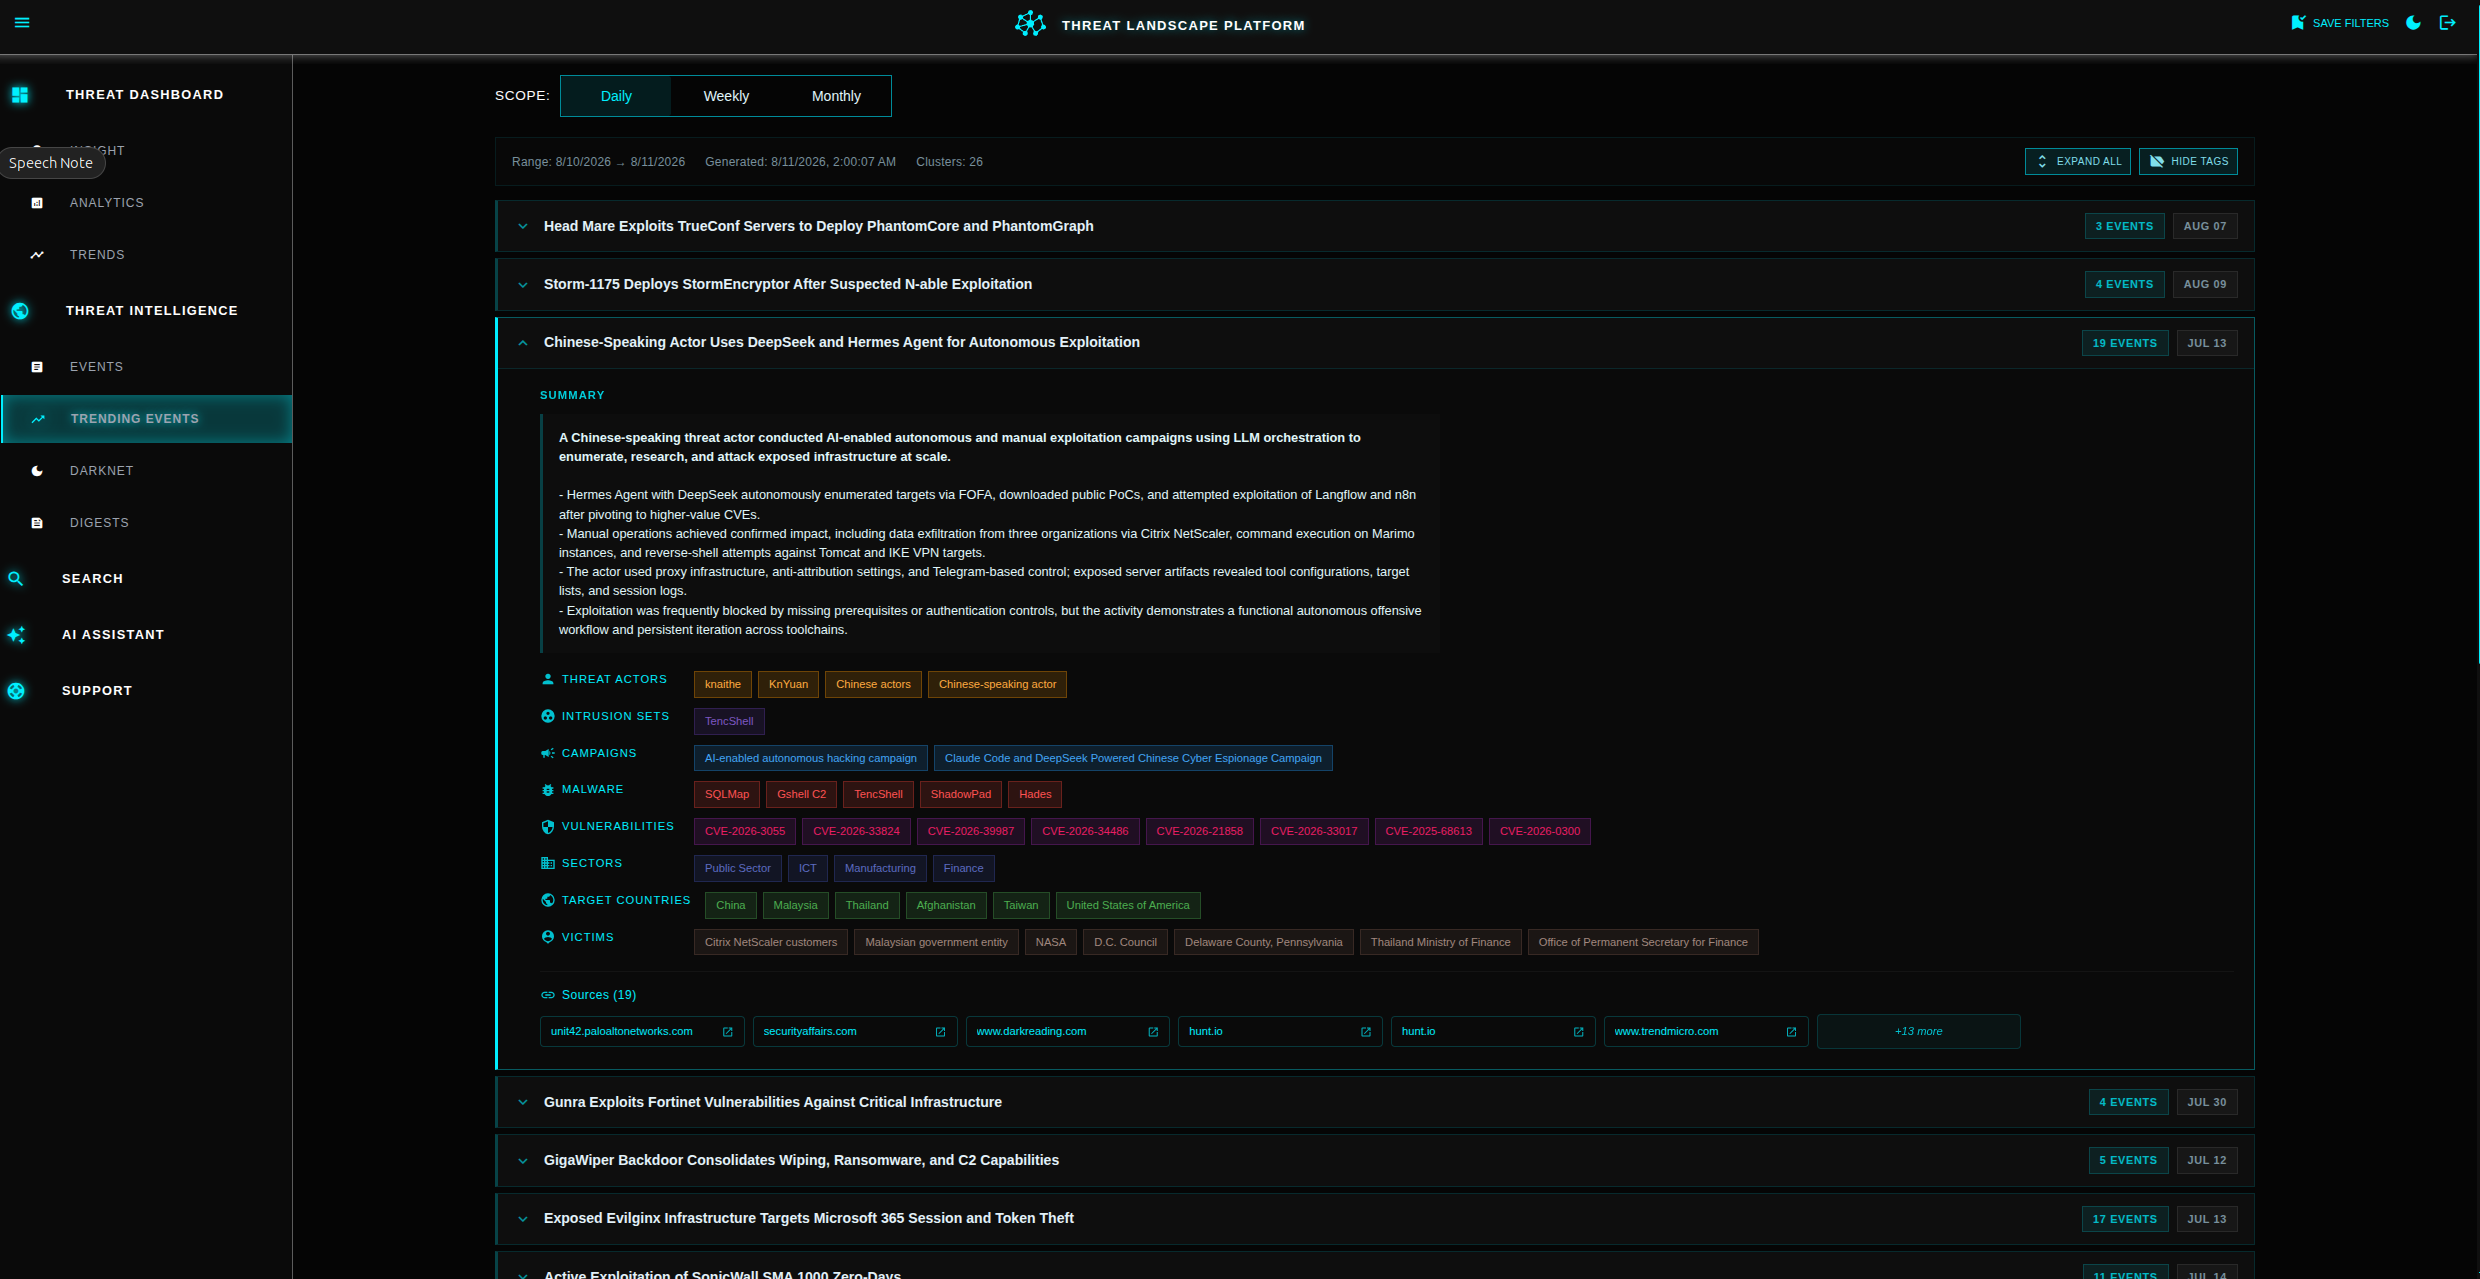
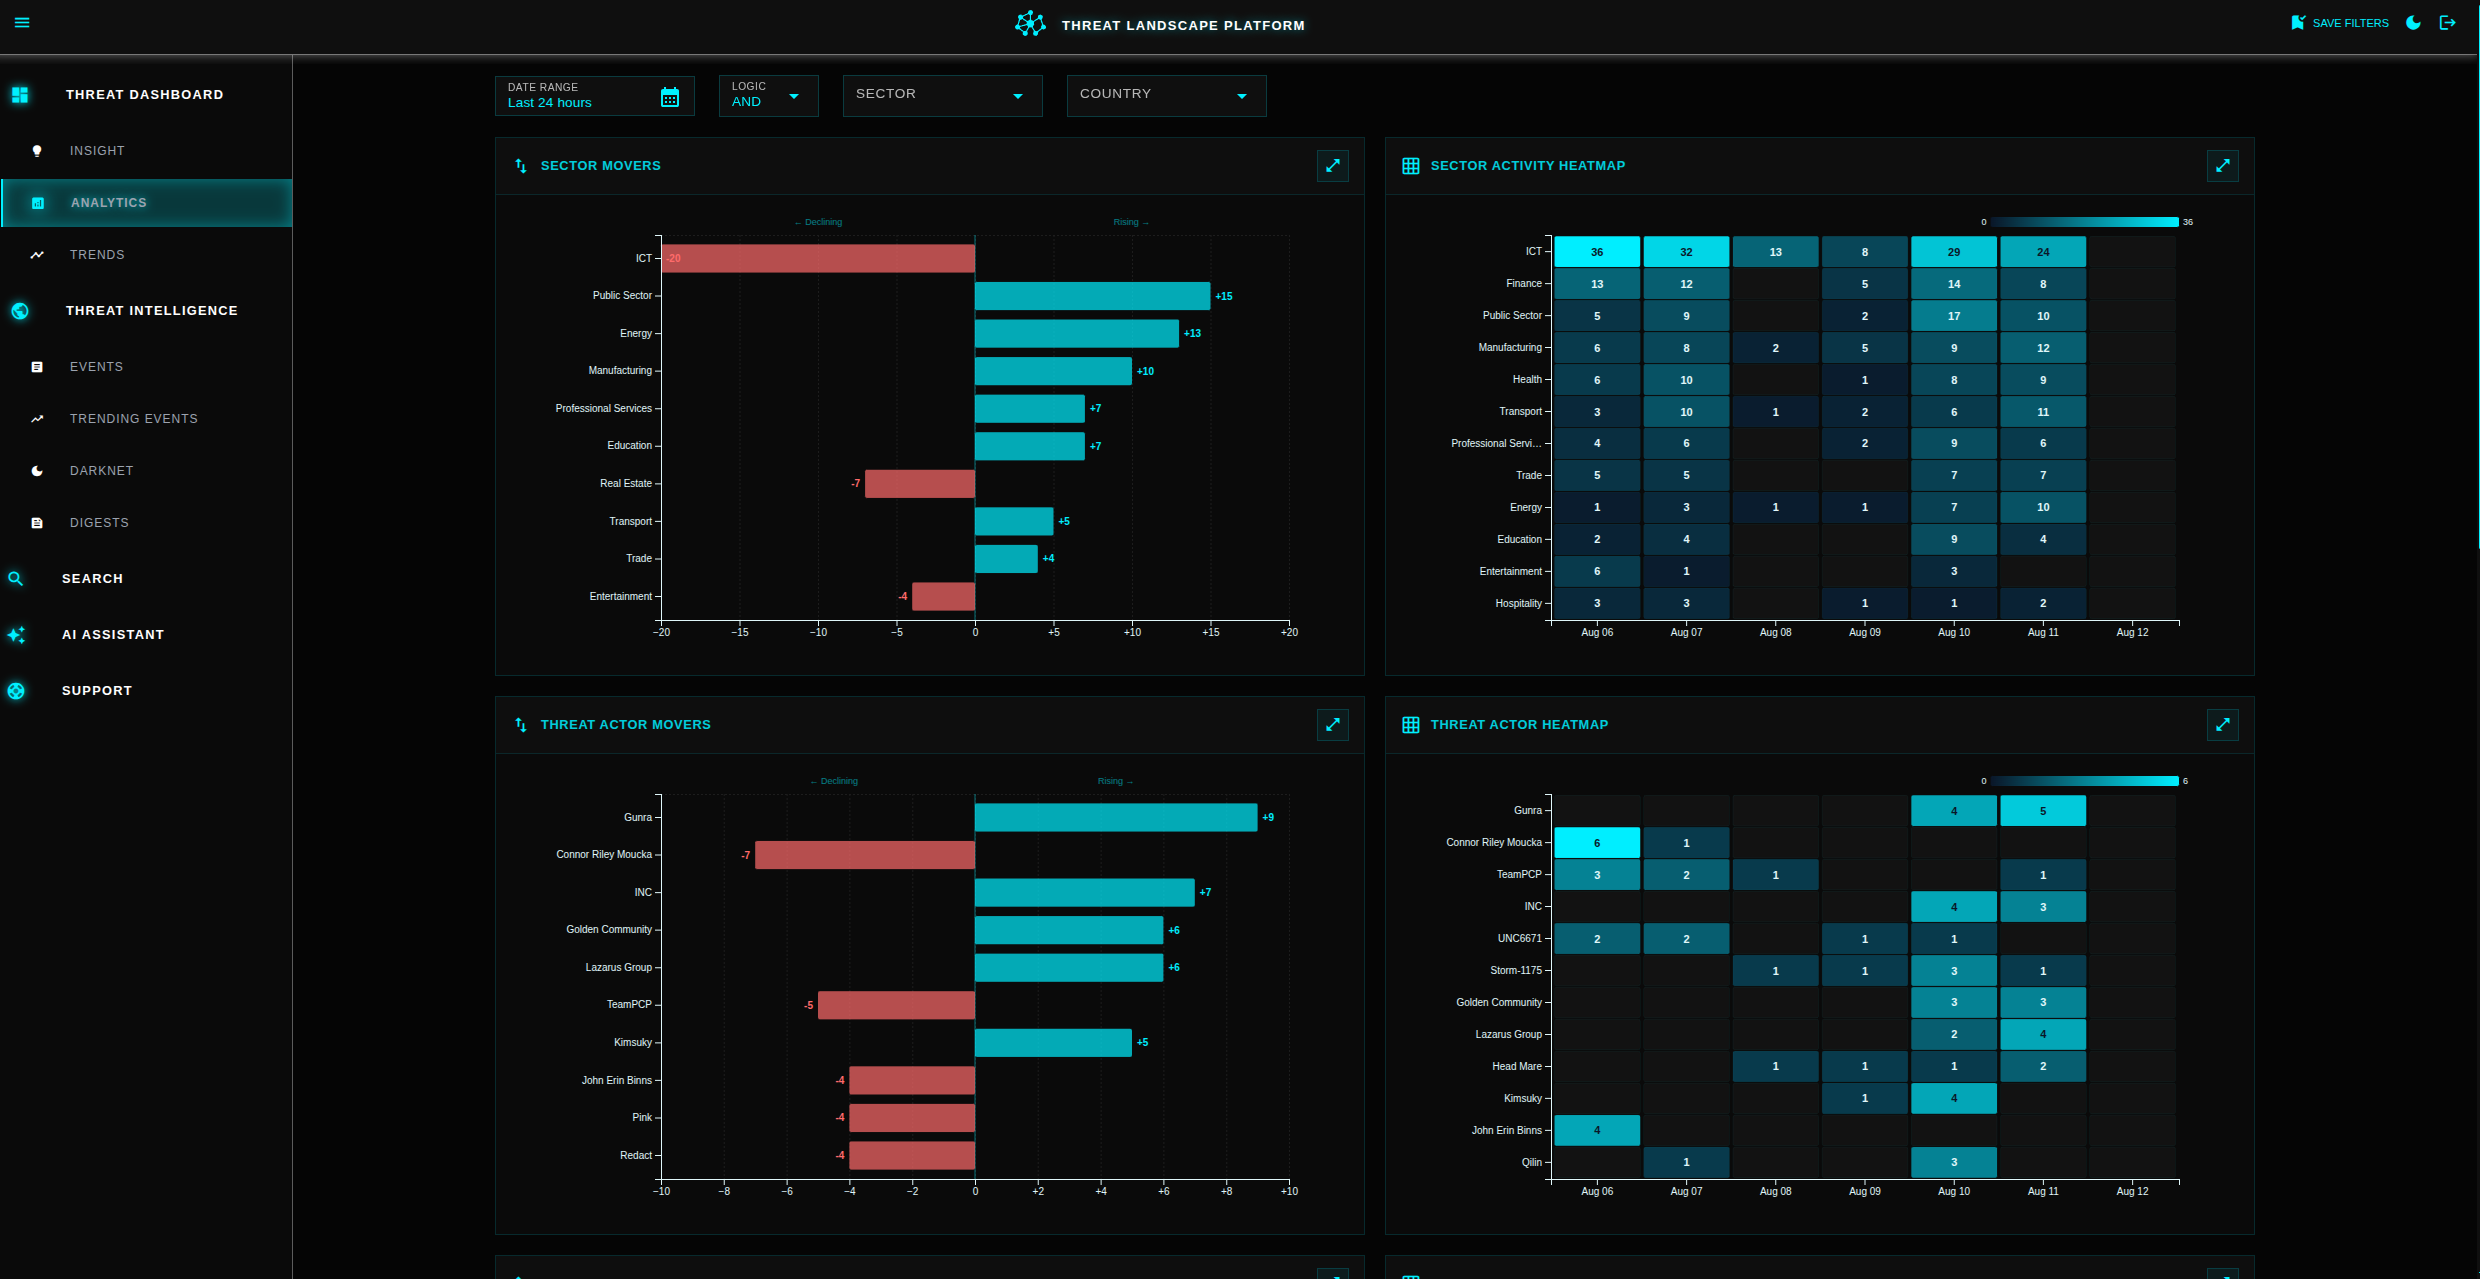
Trend Detection & Early Warning
Identifies emerging threat patterns, surging malware campaigns, and zero-day vulnerability disclosures, with CVEs prioritized by active exploitation so you get early warning before threats become widespread incidents.
Export Options (STIX 2.1, PDF)
Export intelligence in STIX 2.1 bundles for SIEM/SOAR/TIP integration. Generate PDF reports for stakeholder briefings.
Darknet Monitoring & Exposure Discovery
Monitor criminal forums, leak sites, and darknet marketplaces for early signs of targeting, stolen data exposure and supplier mentions relevant to your organization and sector.
Use Cases
How security teams leverage the platform to defend their organizations.
Faster Threat Detection
When security teams are overwhelmed by unstructured reports, critical threats go unnoticed. Automated fact extraction and AI-synthesized triage surface those threats immediately. Analysts skip the manual data processing and focus on high-priority alerts, so detection accelerates and triage time drops by 50-70%.
Incident Response Readiness
When incidents occur, responders often lack the context they need for rapid containment. Visualized threat graphs give instant access to threat actor profiles, known infrastructure, and historical campaigns. IR teams understand adversary capabilities right away, cutting mean time to contain (MTTC) and improving remediation accuracy.
Risk Prioritization
Security teams face thousands of daily alerts and struggle to pinpoint the greatest risks. Filter intelligence by sector, geography, and targeted technologies, then apply confidence scoring and provenance tracking to point resources at validated threats that target your industry and technology stack.
Vulnerability Intelligence & Early Warning
Organizations often hear about newly disclosed CVEs only after exploitation attempts have begun. Continuous CVE extraction and early warning trend detection flag emerging vulnerabilities before widespread exploitation. Teams patch proactively, preventing zero-day compromises and shrinking the attack surface.
Proactive Threat Hunting
Threat hunters often lack searchable intelligence broad enough to proactively hunt for compromise. Advanced search across TTPs, IOCs, and threat actor profiles, all mapped to MITRE ATT&CK, supports targeted, hypothesis-driven hunting. You find known adversary behaviors long before automated detection systems trigger alerts.
Red Team Preparedness
A red team exercise is only as current as the adversary TTPs behind it. Up-to-date adversary playbooks, real-world attack chains, and current malware TTPs are mapped directly to MITRE ATT&CK, so exercises mirror current threat actor capabilities. That improves defensive readiness and validation.
Regulatory & Compliance Reporting
Security and compliance teams often struggle to produce evidence-based threat reports for auditors and regulators. The platform generates PDF reports with full provenance citations automatically, and STIX bundle exports drop into structured compliance frameworks. Auditable, source-backed intelligence helps you satisfy regulatory requirements such as GDPR, NIS2, and DORA and demonstrate clear due diligence.
Cost Prevention through Early Detection
Breaches that earlier threat awareness could have prevented cost organizations significant financial losses. The early warning system detects emerging threats, trending malware, and targeted campaigns against your sector before widespread compromise occurs. Acting on early indicators prevents costly incidents and reduces potential breach costs, downtime, and reputational damage by millions of dollars.
Darknet Risk Monitoring
Signs of targeting often show up in criminal ecosystems long before they surface in mainstream reporting or internal telemetry. Darknet monitoring flags leak-site claims and marketplace listings tied to your brand, sector, suppliers, and technologies. That gives immediate visibility into extortion risks and third-party exposure, for faster validation and response.
Security Automation & Enrichment
Manual IOC extraction and SIEM updating is a slow, error-prone bottleneck. Structured STIX 2.1 intelligence drops directly into your existing security stack. Engineering teams get high-fidelity, pre-correlated threat data that enriches SIEM alerts and triggers SOAR playbooks, so they can orchestrate defenses and block threats at machine speed without human intervention.
Integrations & Export Formats
Intelligence that drops into your existing security workflows.
STIX 2.1
Native STIX 2.1 bundle exports for direct integration with SIEM, SOAR, and TIP platforms. The industry-standard format ensures compatibility.
PDF Reports
Executive-ready PDF reports with full citations and provenance, built for stakeholder briefings and compliance documentation.
Ready to Empower Your Security Team?
See how the Threat Landscape Platform transforms your threat intelligence operations.